Estimated reading time: 5 minutes · Last updated:
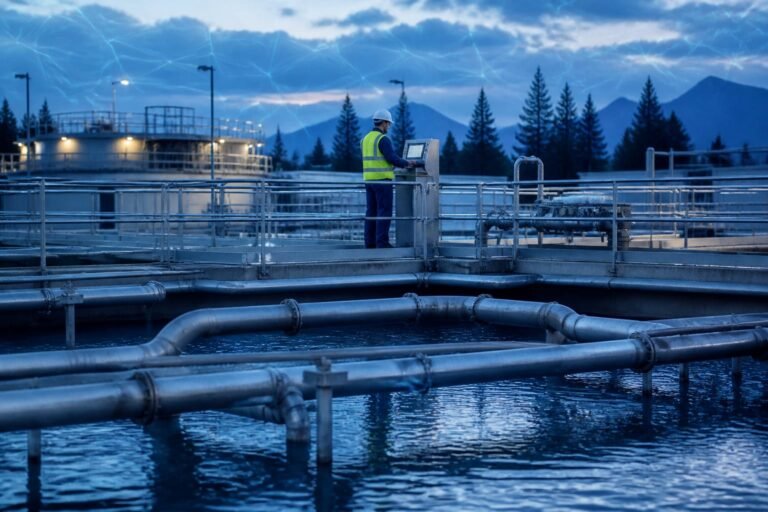
After cyberattacks this summer struck more than 100 public water systems across 12 states, operators and academics say defending treatment plants is an ongoing task. As first reported by Spectrum News, New York has directed millions of dollars and new regulations at drinking water and wastewater facilities to raise baseline protections. Utilities such as the Monroe County Water Authority — whose Shoremont / Shorement plant in Greece serves about 800,000 people and can treat up to 140 million gallons per day — describe the challenge as a function of changing threats and aging operational technology. Operators and state rules now focus on controls such as multifactor authentication, stronger passwords and mandatory incident reporting.
It’s constantly changing, so we're chasing a moving target.
Justin Moore, director of information technology, Monroe County Water Authority
Key takeaways
- More than 100 public water systems in 12 U.S. states were targeted in the summer attacks that prompted renewed focus on plant cybersecurity.
- New York state has allocated millions of dollars and introduced regulations requiring training, multifactor authentication and incident reporting for drinking water and wastewater systems.
- Monroe County Water Authority’s Shoremont / Shorement plant serves roughly 800,000 Western New Yorkers and can handle up to 140 million gallons per day.
- Shoremont received $1 million in federal funding for cybersecurity improvements, and the state has sent tens of millions of dollars to water operators statewide.
- New York State Department of Environmental Conservation records show zero cyberattack incidents reported at water systems since the new reporting rules took effect at the end of March.
Table of contents
- Key takeaways
- What changed this summer: coordinated attacks and higher stakes
- How utilities are adapting operations and systems
- Why smaller and rural plants are most exposed
- Regulation, reporting and the limits of the current response
- How the situation could evolve
- What to be careful about
- Frequently asked questions
What changed this summer: coordinated attacks and higher stakes
Security teams at utilities describe the summer campaign against U.S. water systems as qualitatively different from isolated intrusions. Multiple operators reported that attackers struck systems in a coordinated pattern, and public reporting attributed the campaign to hackers tied to Iran. The scale — more than 100 public water systems across 12 states — pushed plant managers and state regulators to reassess priorities around detection, isolation and recovery.
For operators, the problem is not only the number of incidents but their potential impact. Treatment and distribution rely on operational technology that controls pumps, valves and chemical dosing; compromise of those systems can cause service interruptions or degrade water quality. That risk profile explains why both local utilities and state agencies have moved to tighten rules and to dedicate funding to upgrades.
How utilities are adapting operations and systems
Plant managers say the practical response combines technical changes, staff training and architecture choices that separate critical networks from the internet. Monroe County Water Authority’s IT director says the authority is keeping its control systems on supported technologies, applying patches and requiring stronger access controls. Managers also emphasise network segmentation and air-gapped or isolated optical links where feasible.
Investment accompanies the operational changes. The Shoremont / Shorement plant received $1 million in federal cybersecurity funds this year, and state allocations amount to tens of millions of dollars directed at water operators across New York. Those funds are being used for controls, detection tools and operator training rather than visible upgrades such as new treatment basins — the emphasis is on hardening the digital components that run the plants.
Why smaller and rural plants are most exposed
Experts at Rochester Institute of Technology highlight the uneven readiness across the sector. Smaller systems and rural plants often run older control hardware, have limited IT headcount and operate under tighter budgets. That combination reduces their capacity to deploy multifactor authentication, maintain up-to-date software or run continuous monitoring.
The resource gap creates an asymmetric risk: an attacker needs only one weakness to escalate into operational impact. RIT’s cybersecurity chair says these systems face more pressure to cut costs and often lack the personnel to keep pace with rapidly evolving attack methods, leaving them comparatively vulnerable even as larger authorities boost defences.
Regulation, reporting and the limits of the current response
Governor Kathy Hochul announced new statewide cybersecurity requirements for drinking water and wastewater systems earlier this year, including mandated training, multifactor authentication and complex password rules. The regulations also require utilities to report incidents to the state, and public records from the New York State Department of Environmental Conservation show zero reported attacks at water systems since the reporting rule took effect at the end of March.
Regulation and funding improve the baseline but do not eliminate the threat. Operators acknowledge that tactics evolve and that keeping systems on supported, patchable platforms is a continuous task. As Monroe County leaders and plant staff note, the work is iterative: upgrades and training reduce some exposures, but defenders must constantly adjust to new methods and targets.
| Entity | Role | Relevant figure |
|---|---|---|
| Shoremont / Shorement plant | Monroe County Water Authority treatment facility | serves ~800,000 people; up to 140 million gallons/day |
| Monroe County Water Authority | Regional water utility | third largest in New York state |
| New York state | Regulator and funder | tens of millions of dollars allocated |
| Federal funding to Shoremont | Grant for cybersecurity | $1 million |
How the situation could evolve
The case for
- State regulations requiring multifactor authentication, training and incident reporting will raise minimum protections and create a common compliance baseline.
- Dedicated funding — including the $1 million to Shoremont and tens of millions routed to operators statewide — lets authorities buy monitoring tools, patch legacy systems and train staff.
The case against
- Smaller and rural systems with outdated operational technology and limited IT staff will lag behind larger utilities, preserving exploitable gaps.
- Adversaries acting at scale, including state-linked campaigns, can adapt faster than individual utilities can retrofit legacy control systems, maintaining pressure on defenders.
What to be careful about
- Operational technology (OT) in many plants runs unsupported or older hardware that cannot be patched easily.
- Limited staffing at smaller utilities reduces continuous monitoring and incident response capacity.
- A single exploited vulnerability in a control network can allow attackers to reach critical process systems.
- Regulatory changes improve reporting but do not guarantee timely detection at facilities lacking monitoring tools.
The bottom line
Water utilities face a technical and organisational problem rather than a single fix. The summer attacks accelerated funding and rulemaking in New York and focused attention on controls such as multifactor authentication, training and network isolation. But defenders still contend with legacy control systems, uneven staffing levels and adversaries that can adapt tactics. The outcome will depend on how quickly funding reaches smaller operators, how consistently rules are implemented, and whether utilities can modernise operational technology without disrupting service.
What to watch
- Watch for New York State guidance on enforcement and timelines for the new drinking water cybersecurity regulations; no date has been set.
- Watch for announcements of further state or federal grants aimed at smaller water systems; no date has been set.
- Watch for any public sector advisories or bulletins from the New York State Department of Environmental Conservation about incident reporting or compliance; no date has been set.
Frequently asked questions
How many water systems were hit this summer?
Public reporting and operator accounts point to attacks on more than 100 public water systems across 12 U.S. states during the summer campaign.
What has New York done in response?
Governor Kathy Hochul announced new cybersecurity rules for drinking water and wastewater systems that require training, multifactor authentication and incident reporting, and the state has directed tens of millions of dollars to operators.
Which plants are most at risk?
Smaller and rural facilities are most exposed because they often run older control equipment and have smaller IT staffs, a combination that limits patching and continuous monitoring capacity.
Related reading