Estimated reading time: 5 minutes · Last updated:
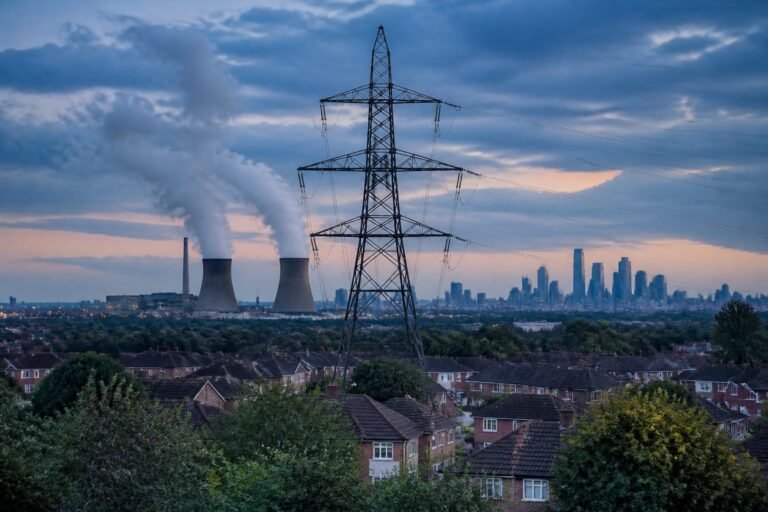
Energy cybersecurity is driven today more by human attackers exploiting decades-old control systems than by hypothetical rogue AI. As first reported by The Verge, reporter Justine Calma spoke with Joshua Corman of the Institute for Security and Technology, who identified ageing operational technology, orphaned equipment and slow update cycles as the core weaknesses. The average age of a U.S. nuclear reactor is about 44 years, and many OT devices were not built for internet-era threats. Corman added that generative AI acts as a force multiplier, lowering the skill barrier for attackers and speeding reconnaissance and exploitation.
This has been a force multiplier and continues to grow.
Joshua Corman, executive in residence for public safety and resilience at the Institute for Security and Technology
Key takeaways
- Aging infrastructure: The average age of a U.S. nuclear reactor is about 44 years, leaving equipment that was not designed for internet connectivity exposed.
- Industry voices: Joshua Corman of the Institute for Security and Technology says AI has been 'a force multiplier' for attackers.
- Scale of community utilities: Rob Denaburg represents the American Public Power Association, which covers community-owned utilities across 2,000 municipalities.
- Defender funding: OpenAI pledged $1 billion on 3 September 2026 toward tools and training intended to help defend critical infrastructure.
Table of contents
- Key takeaways
- Why decades-old control systems remain the central weak point
- How generative AI changes attacker capabilities — and defender priorities
- Policy gaps, vendor responsibility and practical steps for utilities
- How the next 12–24 months could unfold
- What to be careful about
- Frequently asked questions
Why decades-old control systems remain the central weak point
Utilities run operational technology (OT) that often predates modern networking and cybersecurity design. Many control systems were built for long lifespans and local operation; the average age of a U.S. nuclear reactor is about 44 years, and other power-plant equipment can be similarly old. That longevity matters because manufacturers that wrote the original firmware or management software sometimes no longer exist, leaving 'orphaned' devices with no vendor to issue security patches.
Applying updates in OT is also slower and riskier than in IT. Devices may be designed for quarterly or annual updates, and operators avoid frequent changes because an erroneous patch can interrupt generation or harm equipment. Smaller utilities commonly lack staff or budget to run continuous monitoring and rapid-response programs, so basic mitigations — network segmentation, strict access controls, or the ability to switch to manual operation — are unevenly implemented. The result is many attack paths that rely on human misconfiguration, unpatched components or weak administrative controls.
How generative AI changes attacker capabilities — and defender priorities
Joshua Corman said generative AI does not yet replace a motivated human adversary, but it amplifies what humans can achieve. He said AI speeds reconnaissance, automates the writing of exploit code and helps chain vulnerabilities together. Corman, who serves as the Institute for Security and Technology's executive in residence for public safety and resilience, characterises the effect as a force multiplier that lets 'any sociopath that wants to [attack]' be more effective than before.
That amplification means lower-skilled attackers can attempt assaults that previously required sophisticated nation-state tradecraft. But defensive measures remain largely the same: stop initial access, segment OT from IT, patch where feasible, and be able to revert to manual controls. Rob Denaburg, cybersecurity program senior manager at the American Public Power Association, stresses that "as long as you can stop them in one spot, they can't carry out that attack," underlining that preventing a single pivot or privilege escalation can break an adversary's chain even when AI helped build it.
Policy gaps, vendor responsibility and practical steps for utilities
Government policy and AI developers both have roles to play. Sophie McDowall of the Foundation for Defense of Democracies’ Center on Cyber and Technology Innovation argues there are fewer guardrails around AI research and deployment than exist for hazardous sectors such as nuclear technology. OpenAI's 3 September 2026 pledge of $1 billion to subsidize training and model access for defenders is one industry step, and Sam Altman's recent outreach to utilities on 10 September 2026 demonstrates a willingness by some model developers to engage directly.
Still, practical steps for utilities do not depend on novel AI tools. Operators can reduce risk by hardening remote access, enforcing least privilege, maintaining network segmentation, testing manual failover, and prioritizing patches for the most exposed systems. In some cases, disconnecting nonessential internet-facing services or limiting interconnections is the safest short-term move. McDowall also highlights a research gap: more work is needed on how AI can help defenders beyond red teaming, and on governance that balances innovation with restrictions where infrastructure safety is at stake.
How the next 12–24 months could unfold
The case for
- OpenAI's $1 billion commitment could accelerate access to defensive models and subsidized training for utilities, improving threat detection and incident response.
- Wider adoption of basic OT hygiene — segmentation, manual failover plans and prioritized patching — can materially reduce the number of exploitable paths even if attackers use AI tools.
The case against
- Orphaned and decades-old OT devices with infrequent update cycles will remain vulnerable and difficult to remediate at scale for smaller utilities.
- As generative models proliferate, less-skilled attackers can mount more effective campaigns, increasing the volume of probing and attempted intrusions that defenders must triage.
What to be careful about
- Utilities with quarterly or annual OT update cycles risk long exposure windows for known vulnerabilities.
- Small community utilities lacking dedicated cybersecurity teams face staffing and budget shortfalls that delay mitigations.
- Relying on AI-driven defensive tools risks introducing control and validation problems in sensitive OT environments.
The bottom line
The immediate cybersecurity threat to energy systems is human adversaries exploiting long-lived control systems that were not designed for modern networks. Generative AI increases the speed and scale at which attackers can discover and weaponise vulnerabilities, but it does not change the core defensive priorities: prevent initial access, segment and isolate OT, maintain tested manual failovers, and prioritise fixes for the most exposed assets. Industry commitments such as OpenAI's 3 September 2026 pledge can help defenders, but governments, model developers and utilities must align on safeguards, research funding and operational constraints to keep that assistance from introducing new hazards.
What to watch
- Watch for federal or state rulemaking that would set safety or research limits for AI applied to critical infrastructure; no date has been set.
- Watch for industry rollouts and independent audits of AI-assisted defensive tools after OpenAI's 3 September 2026 pledge; no date has been set.
Frequently asked questions
Is rogue AI the main threat to power grids?
No. Joshua Corman says human attackers exploiting legacy systems remain the primary threat; many control devices predate modern security, and some U.S. nuclear reactors average about 44 years in age.
How does AI change attacker behaviour?
Generative AI lowers the skill barrier by automating reconnaissance and exploit development, a dynamic Joshua Corman describes as a force multiplier that makes less-skilled adversaries more effective.
Can AI help defend grids?
Possibly. OpenAI pledged $1 billion on 3 September 2026 to subsidize defender training and access, but Corman cautioned that integrating AI into operational technology requires care because introducing rapid change in OT environments can create new risks.
Related reading